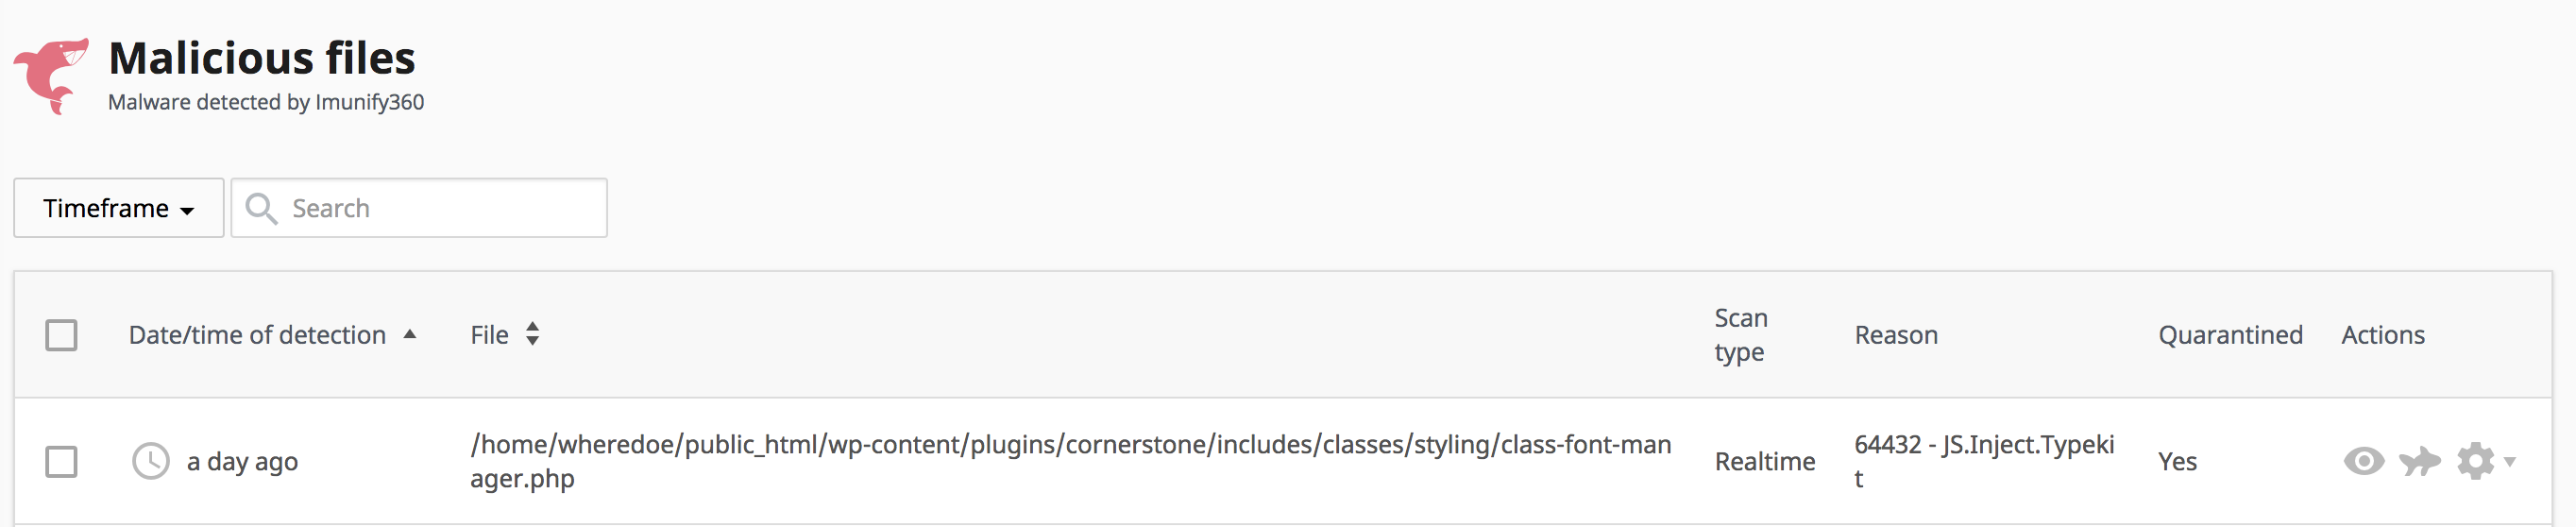
This has happened with two different hosting companies with two different clients. One is SiteGround and the other is LightningBase. When updating, for whatever reason the file “class-font-manager.php” is updated with both group and owner set as root and 000 as the permission (no read/write/execute). This causes a 500 server error and I’ve had to go in and manually delete the file on the server, then upload it again manually. Here is the line in my error log that shows the issue. It has happened for the last several updates for two of my clients.
[29-Jul-2018 00:02:48 UTC] PHP Fatal error: require_once(): Failed opening required ‘/home/xxxxx/public_html/wp-content/plugins/cornerstone/includes/classes/styling/class-font-manager.php’ (include_path=’.:/opt/cpanel/ea-php70/root/usr/share/pear’) in /home/wheredoe/public_html/wp-content/plugins/cornerstone/includes/cornerstone-plugin.php on line 105
I’m wondering if it’s related to this thread: https://theme.co/apex/forum/t/malware-found-in-cornerstone-update/39594. Maybe something in that file is flagging anti-virus software on the servers?
Actually, it’s definitely that. Can something be rewritten to inject the typekit code in a different way?